Is the transition to Post-Quantum Cryptography a critical step toward cyber resilience, or does it create more concern than actual danger?
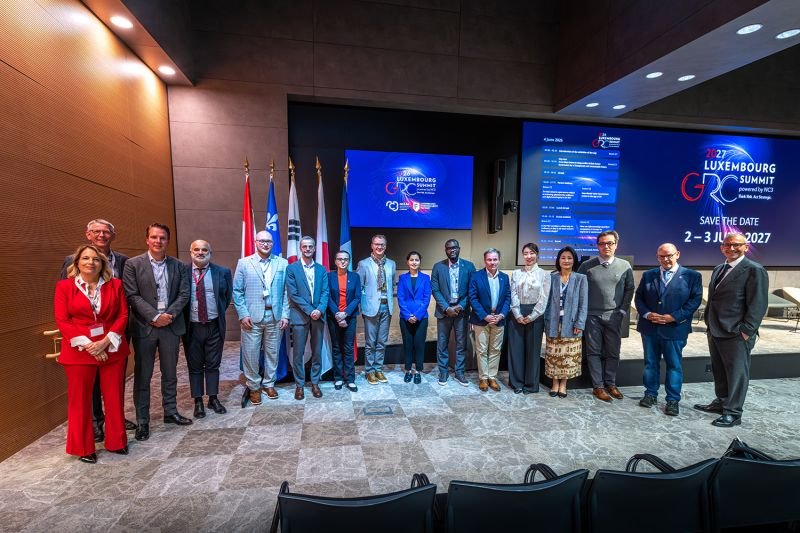
This question was at the center of a forum moderated by LuxQuantum during the 2nd Luxembourg GRC Summit 2026, bringing together perspectives on cybersecurity, governance, risk, compliance, and the transition toward quantum-safe security.
The discussions highlighted an important reality: preparing for the quantum era is not simply a matter of replacing cryptographic algorithms.
It is increasingly a question of governance, risk management, technological adaptability, and long-term cyber resilience.
Why the PQC transition matters
Organizations rely on cryptography throughout their digital infrastructure — across applications, communications, identities, data, networks, and cloud environments.
As quantum technologies develop, organizations need to understand where cryptography is used today and how their security architecture can evolve toward quantum-safe mechanisms.
This makes cryptographic visibility an important starting point.
Before organizations can build an effective transition strategy, they need to understand their existing cryptographic environment, dependencies, and potential exposure.
From migration to crypto-agility
The transition to PQC should not be viewed simply as a one-time replacement of existing algorithms.
Technologies, standards, regulations, and security requirements will continue to evolve.
Organizations therefore need crypto-agility: the ability to adapt cryptographic mechanisms as requirements and technologies change without repeatedly redesigning the underlying infrastructure.
This changes the question from:
“How do we migrate to PQC?”
to:
“How do we build a security architecture capable of evolving over time?”
Governance and risk are part of the transition
Quantum readiness is not solely a technical responsibility.
The discussions at the GRC Summit reinforced the importance of bringing quantum-safe preparation into broader governance, risk, compliance, and resilience strategies.
Organizations should increasingly consider:
Cryptographic visibility — understanding where and how cryptography is deployed.
Crypto-agility — creating the ability to adapt as standards and technologies evolve.
Regulatory readiness — preparing security architectures for emerging requirements.
Long-term risk assessment — evaluating quantum-related risks before they become urgent operational problems.
Practical transition strategies — moving toward quantum-safe security in a manageable and interoperable way.
Understanding Contracts and Agreements
Contracts are essential for establishing clear expectations and protecting your interests in business relationships. Whether you are hiring employees, working with suppliers, or partnering with other businesses, a well-drafted contract outlines the terms of the agreement and minimizes the risk of misunderstandings.
Common contracts every business should have include:
- Employment Agreements: Define roles, responsibilities, and confidentiality for your team members.
- Vendor Contracts: Specify payment terms, delivery schedules, and other details when working with suppliers.
- Partnership Agreements: Clarify roles, profit-sharing, and decision-making processes for co-founders or business partners.
When in doubt, consult a legal professional to draft or review your contracts to ensure they meet your needs and comply with local laws.
The role of hybrid quantum-safe security
At LuxQuantum, we see the transition as an evolution rather than an overnight replacement of existing infrastructure.
Our work focuses on PQC readiness, quantum-safe architectures, and the hybridization of Post-Quantum Cryptography (PQC), Quantum Key Distribution (QKD), and classical cryptography.
Bringing these approaches together can help organizations develop security architectures that evolve as technologies, standards, and risk requirements change.
The objective is not simply to deploy another security technology.
It is to create the foundations for long-term cryptographic resilience.
Building quantum resilience together
The Luxembourg GRC Summit demonstrated the importance of collaboration between academia, industry, cybersecurity experts, policymakers, and the public sector.
Preparing for the quantum era will require this kind of collaboration.
For organizations, the important question is increasingly not whether cryptographic infrastructure will need to evolve, but how to make that transition controlled, interoperable, and resilient.
At LuxQuantum, we look forward to continuing these conversations and contributing to a secure and quantum-resilient future.ness.